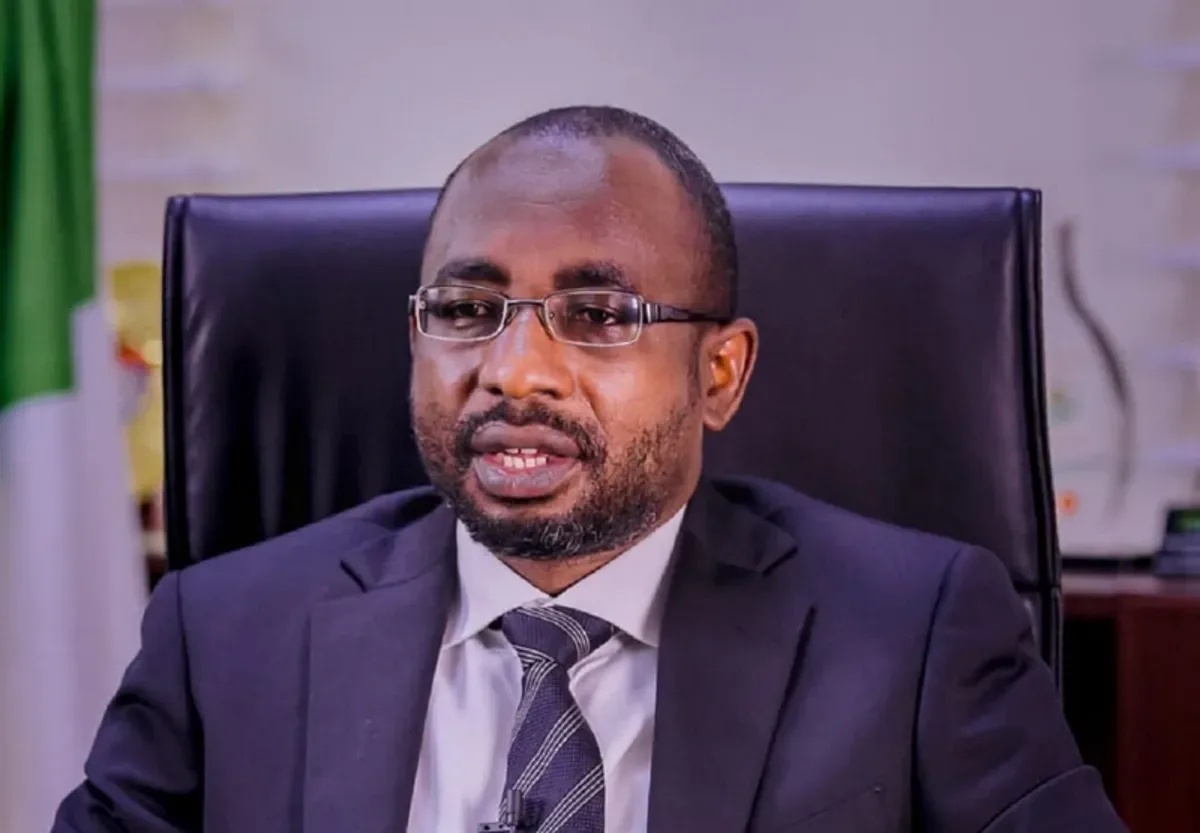
NITDA Director-General, Kashifu Inuwa Abdullahi, disclosed the policy at a cybersecurity awareness webinar organised by the Nigeria Internet Registration Association (NiRA) through its .ng Academy. The event was held as part of activities marking Cybersecurity Awareness Month under the theme, “Securing Nigeria’s Digital Foundation: DNSSEC, the .ng Domain, and the Future of National Cyber Resilience”.
Represented by Oluwasegun Falayan, Abdullahi said DNS security would become part of the agency’s assessment of cybersecurity readiness across government institutions. He emphasised that protecting government domain names should go beyond simply registering them.
DNSSEC is an extension of the Domain Name System, which helps internet users access websites by translating domain names into numerical addresses understood by computers. It adds digital signatures to DNS records, allowing systems that validate those signatures to check whether responses are authentic and have not been altered.
NiRA President, Adesola Akinsanya, described the technology as an important security layer for Nigeria’s digital infrastructure, particularly amid growing cyber threats. However, he warned that poor implementation could create technical difficulties, including preventing users with DNSSEC-validating systems from accessing affected websites.
Akinsanya explained that DNSSEC does not encrypt internet traffic, stop distributed denial-of-service attacks or protect against compromised domain registrar credentials. He said it should therefore be deployed alongside other cybersecurity measures rather than treated as a complete security solution.
He also called for stronger cooperation among government agencies, internet service providers, domain registrars, businesses and cybersecurity professionals to improve the protection of Nigeria’s domain name infrastructure.
Highlighting the financial and operational consequences of cybercrime, the NiRA president cited figures attributed to Check Point, which indicated that Nigerian organisations faced an average of about 4,361 attempted cyberattacks weekly in June, compared with a global average of approximately 2,270.
He also referred to Nigeria Inter-Bank Settlement System (NIBSS) figures showing that digital payment fraud reached ₦25.85 billion in 2025, despite a decline in the number of reported incidents. He cautioned that fewer reported cases do not necessarily mean that digital systems have become safer, as underreporting could affect the figures.
The NiRA president urged government institutions to review the security of their domain names, strengthen control over account access and activate multi-factor authentication to reduce the risk of unauthorised changes.
The latest directive follows Nigeria’s unveiling of DNSSEC for the .ng domain in April 2026. The initiative, led by NiRA, which manages Nigeria’s country-code top-level domain, was introduced as part of broader efforts to improve trust and security across the country’s internet infrastructure.
By incorporating DNSSEC into its cybersecurity assessment framework, NITDA is seeking to encourage government institutions to adopt stronger safeguards for their online platforms and contribute to a more secure digital environment.
Reporting by TalkNaijaMedia
Reader Comments (0)
No comments yet. Be the first to share your perspective on this report.